

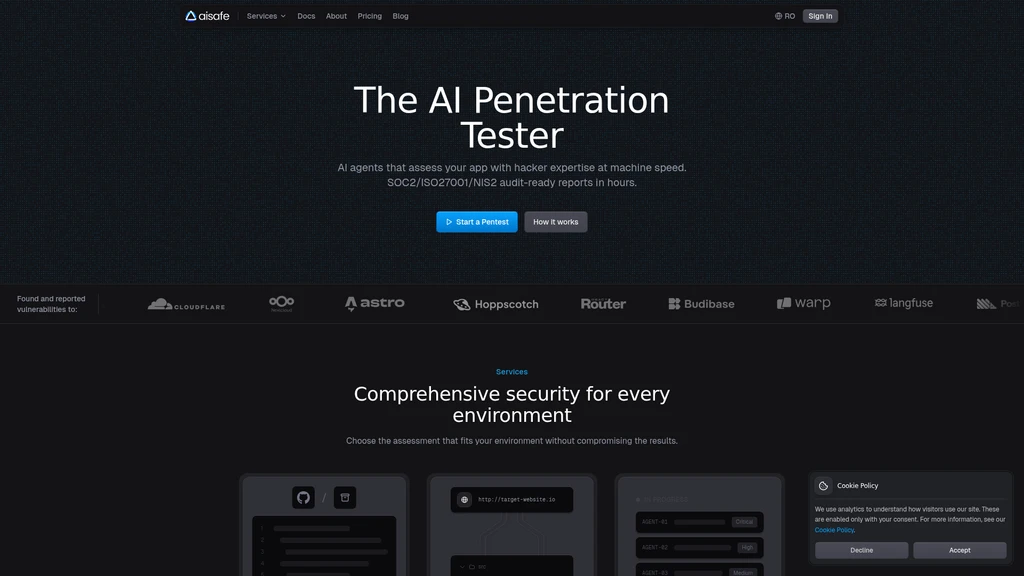
AISafe Labs AI Penetration Tester - AI agents that assess your app with hacker expertise at machine speed. SOC2/ISO27001/NIS2 audit-ready reports in hours.
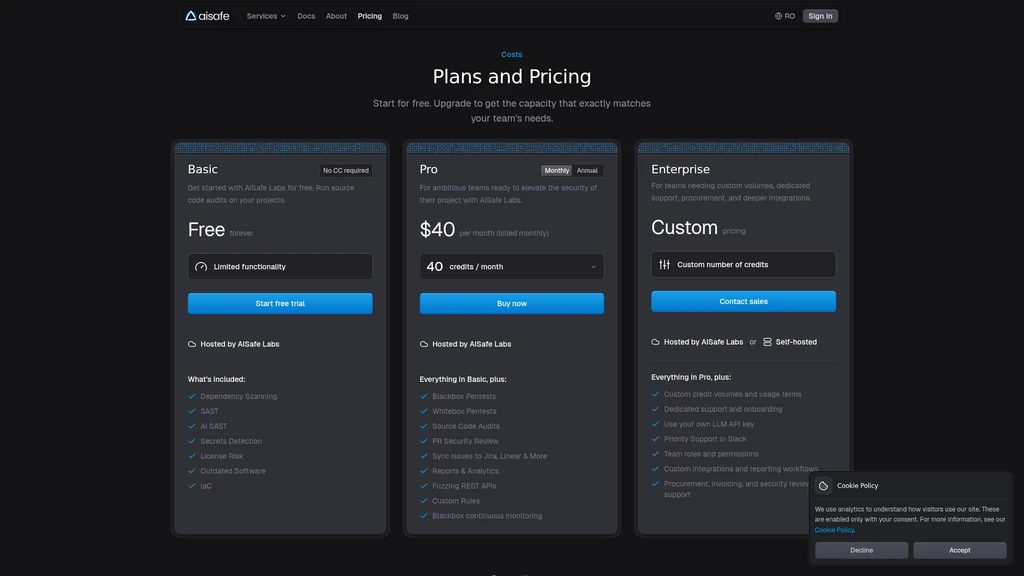
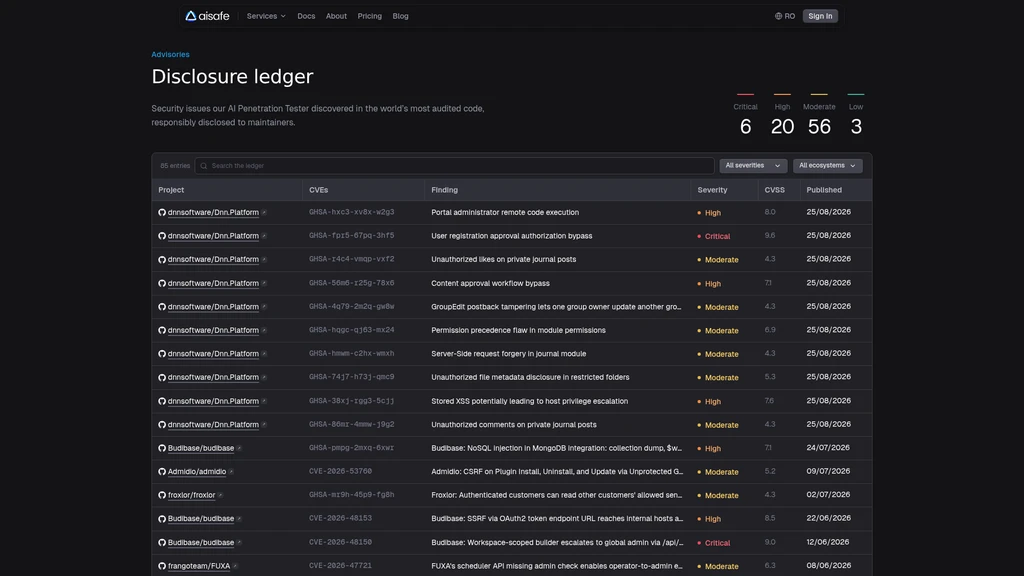
Launched on Sep 9, 2026AISafe Labs is an AI-powered automated penetration testing platform that uses specialized AI agents to conduct security assessments for web and application environments. It is designed for development, security, and compliance teams that need fast, validated vulnerability findings without the long turnaround times of traditional manual pentests. The platform produces audit-ready reports that support SOC 2, ISO 27001, and NIS 2 compliance processes, reducing cost compared to standard manual testing.
Related Content

Copy.ai Review 2026: AI Copywriting Made Easy
Our honest Copy.ai review for 2026. We test Content Agents, AI Workflows, pricing ($29-$249/mo), and compare it to Jasper and Writesonic. Find out if it's worth it for your marketing team.

Rytr Review 2026: Is This Budget AI Writer Worth It?
Our hands-on Rytr review for 2026. We test features, pricing, content quality, and compare it to Jasper & ChatGPT. Find out if Rytr is the best budget AI writing tool.

Word Changer - Free AI tool to rewrite and improve your writing instantly
Writing always using repetitive words or need to avoid plagiarism? Word Changer is a free AI writing assistant that instantly rewrites any text with richer vocabulary and appropriate tone. Get multiple versions with one click, adjust formality level, check readability - all for free!

Unite - AI-powered platform for romantic fantasies and dream couple moments
Explore romantic fantasies and create special moments for your dream couple. This AI-powered platform lets you generate personalized romantic content and experience exclusive AI-created romantic experiences.
Comments